Oct 20 2026
Security

How Project Lightwell Protects the Modern Open-Source Enterprise From Emerging Threats

Red Hat and IBM’s new $5B collaboration promises a safer, more secure future for open-source software and the modern enterprise it empowers.

Open-source software powers much of the modern enterprise but securing it has become increasingly difficult. Organizations often depend on thousands of open-source components, while artificial intelligence is accelerating both the discovery of software vulnerabilities and the speed at which attackers can exploit them. Project Lightwell, a joint initiative from IBM and Red Hat, aims to close that gap by combining AI, coordinated vulnerability remediation and a global engineering workforce to identify, validate and deliver security fixes at enterprise scale. 

When IBM and Red Hat announced Project Lightwell in late May, they committed $5 billion and more than 20,000 engineers to the initiative. At its core is a trusted enterprise clearinghouse designed to help organizations move beyond simply identifying vulnerabilities and toward deploying tested, production-ready remediation across the open-source software supply chain. The initiative also quickly attracted a prominent group of early adopters, including Bank of America, BNY, Citi, Goldman Sachs, JPMorganChase, Mastercard, Morgan Stanley, Royal Bank of Canada, State Street, Visa and Wells Fargo. IBM expects the network to grow to 1,000 organizations by the end of the year. 

Project Lightwell will “define a new industry model, one that brings together AI, engineering expertise and trusted collaboration to secure open-source software at its source and across the entire supply chain,” IBM Chairman and CEO Arvind Krishna states in a press release. “This is about strengthening trust in the systems that power business, government and society.” 

In a conversation with BizTech, Red Hat’s Ben Breard, senior principal product manager for Project Lightwell, discussed why the initiative is needed now, how AI is changing the economics and urgency of open-source security and what Project Lightwell could mean for enterprises that depend on open-source software. 

Click the banner below to read the recent CDW Cybersecurity Research Report. 


BIZTECH:  What was the driving need behind the Project Lightwell collaboration? 

BREARD: Several things happened all within a very close time frame, probably the biggest being what we call the “Claude Mythos moment” that a lot of people had once they had access to it. We realized that a lot of the traditional metrics and security vulnerability tracking — basically the status quo — was heavily challenged, unlike anything previous challenges. We’ve always had a growing volume of CVEs (Common Vulnerabilities and Exposures) that were difficult to handle, but now we were seeing, just from the patching process alone, the volume grow so quickly since bad actors could access Mythos.  

First, it brought unknown vulnerabilities to new code it delivered, which most users didn’t know or understand. Second, bad actors could now chain together low-severity things that devalued the existing threat rating system that software providers rely on to determine where to focus their resources and time on security fixes. All of this really changed the risk profiles enterprise customers see across their estates.  

On the other side with AI, the time to exploit has dropped to almost negative. Five years ago, it was about a one- to two-year window, and a small number of CVEs were exploited. We don’t live in those times anymore. Both companies heard very loudly from our customers, “We need help.” The so-called library space of publicly disclosed cybersecurity flaws and vulnerability catalogs is absolutely massive today. Companies like Red Hat and IBM have done a really good job over the course of our companies’ histories focusing at the platform level and have robust practices around that.  

When you start to look at these scans, all of a sudden, the library space is this glaring void of risk. Seeing that made it clear there’s a serious problem that we have an opportunity to solve. 

BIZTECH: Explain how it works. 

BREARD: It starts with the various communities that make the code libraries we all know and depend on, from all applications basically, with shared common building blocks. Lightwell’s central clearinghouse serves as a security coordination layer and leverages advanced AI capabilities to validate and test fixes across an unprecedented volume of open-source code. Right now, members with frontier AI models are giving us their top prioritized findings, all anonymized.  

As that happens, we come back to queueing theory and how you approach things, or what you can do at different speeds to achieve the maximum throughput — all of those have been codified into our build systems. From there, we either put a patch on a particular version — that’s the lowest-hanging fruit — or we’ll create new code, test it, put it through various test harnesses and then ask the member to see whether it breaks their application. Volume matters, but quality matters more because if you have a high volume of bad code, it’s not worth anything. The number of quality gates we have today is something I’m really proud of. 

Once we complete the code fixes, they go out to the entire Lightwell network, which includes members beyond the clearinghouse who can take advantage of all of the content available within Lightwell. The more members that join at this tier and at the frontier tier, the sooner we’ll start to see this flywheel effect of patched content that can be delivered to everybody. We’re also handling the disclosure, the reporting, and trying to shepherd through fixes and vulnerabilities, not just report them on the CVE side, and are working with the communities to get it all accepted back upstream. We are looking at taking on more members after meeting current capacity demands. We’ll probably adjust requirements a bit as we go because we want the input here to be as big as possible. 

LEARN MORE: How can businesses enhance security for legacy applications?

BIZTECH: Would vendor partners have come together so readily to solve this a few years ago?

BREARD: Marketplace need and alignment on the problem is what drives that good behavior. When you all see the same problem space, and people connect what we’re doing with what they’re doing, everything has value, and people win. If there were no Lightwell, everybody would keep paying for tokens to do the same work and not share it back. That just fractures everything, and we’re all doing the same work over and over again. With this, we use smarter economics to solve things once.  

BIZTECH: Are there other factors driving this kind of collaboration? 

BREARD: A lot of large shops don’t want the risk. Once they know and discover these vulnerabilities, all of a sudden, they have risk on their hands. There are definitely a lot of dynamics at play, but everything revolves around open source right now, and this collaboration is essentially how communities operate within open source. Essentially, Project Lightwell is that, pushed to another scale. When you think about why collaboration is so important, it’s important down the entire value chain of open source, from the very building blocks to the absolute top of patch development and pushing that out. This is the next evolution of that kind of collaboration, extended to a very specific purpose to solve a very real, global problem. I live for this stuff. 
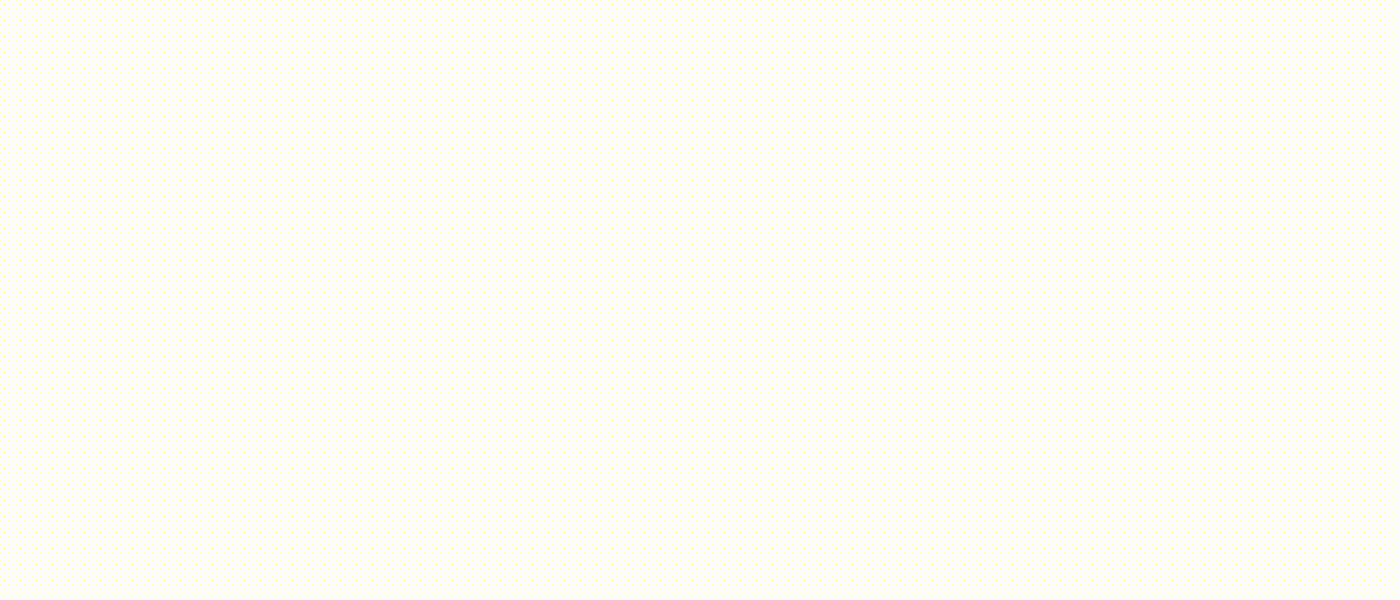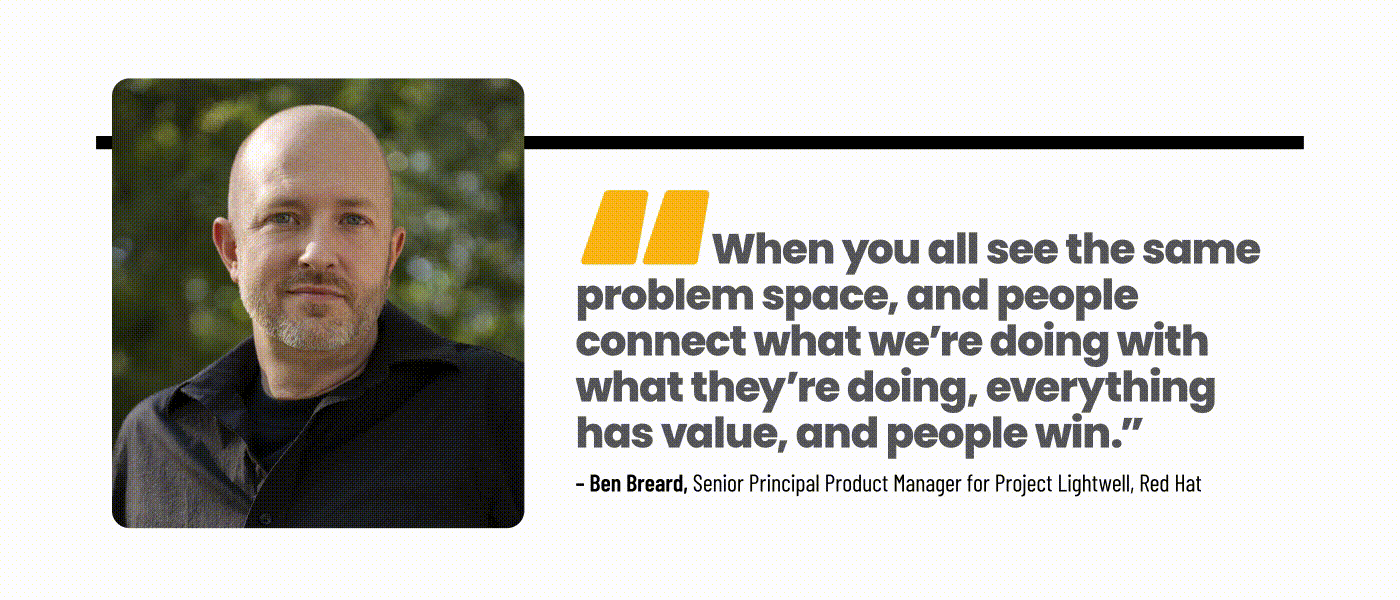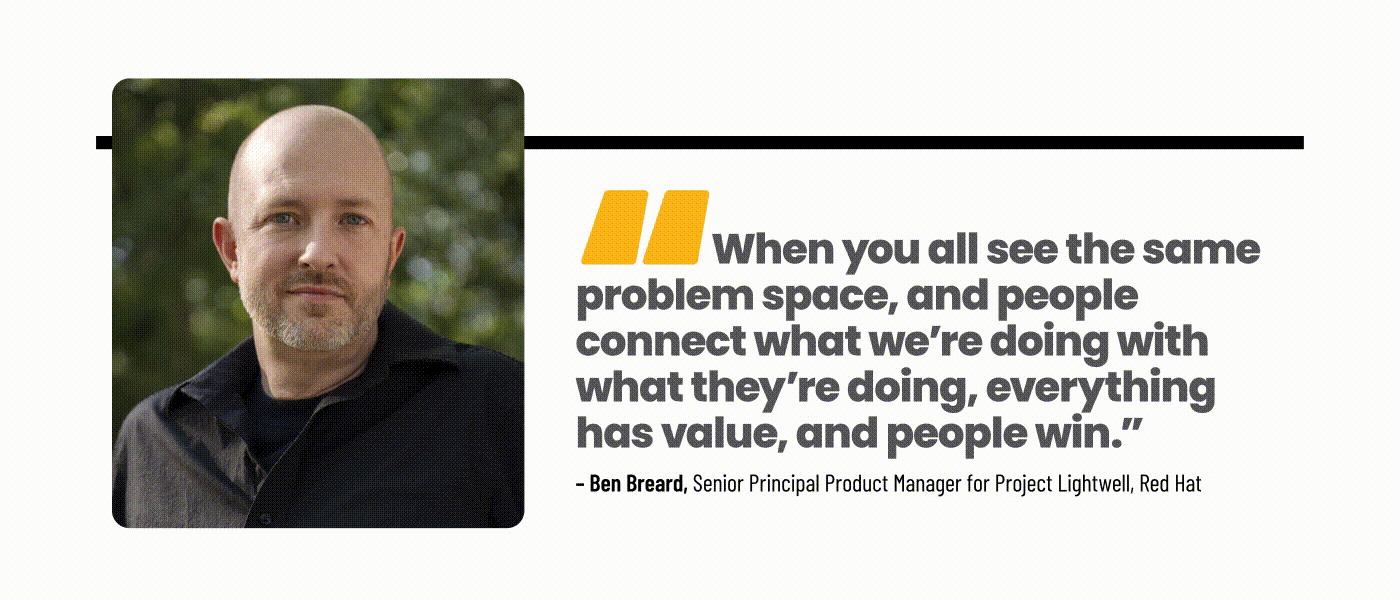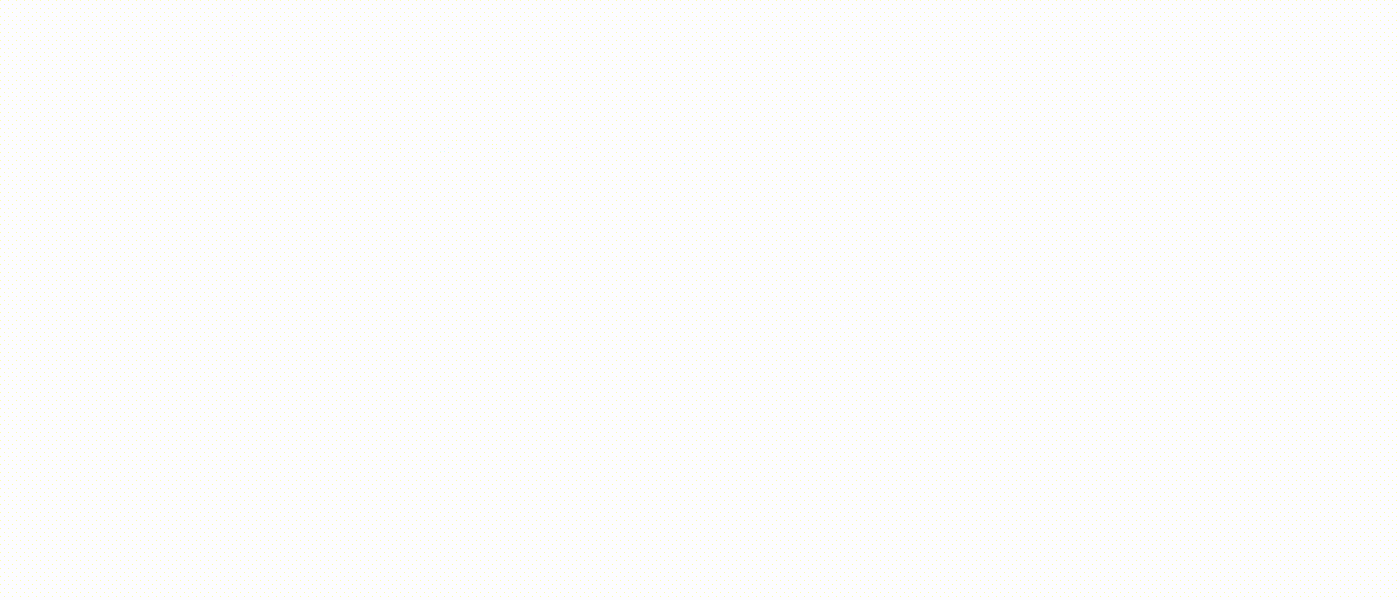
Ben Breartd, Red Hat

BIZTECH: It’s also important that this comes from industry, right? 

BREARD: We’ve definitely talked with a lot of government agencies about Lightwell, most of them are familiar with what we’re doing in the space. We have strong connections there, not just in North America but also everywhere else, in Europe and Asia Pacific. We’re trying to take a global approach.  

BIZTECH: And we’re all safer in the face of emerging threats? 

BREARD: You can’t quantify that. Given the high number of novel vulnerabilities out there, we help customers move beyond how they patched systems five years ago, where you had to wait until a vulnerability was known, and went through the traditional process of report, fix, submit, go out in a release, then test within their own time frames. We actually compress that so that Lightwell network or clearinghouse members have access to patched code 14 days before it’s announced to the project or made visible. It’s necessary when the exploit time has shrunk down so low.  

DISCOVER: Learn why it’s so difficult to measure the return on your artificial intelligence investments.

BIZTECH: What are you seeing now that the collaboration is operational, despite it being early days? 

BREARD: The sense of mission and common perspective on the problem has been amazing. Lightwell gives us the framing to go and solve these challenges, so it’s been really powerful on the customer side as well as the ecosystem side, and internally at the engineering level — the creativity and innovation that these types of time box problems require and are very urgent to solve has just pushed teams to find new creative ways to solve problems. That’s kind of our rallying mission. More specifically, in just the time we’ve been working on Lightwell, to see the amount of content we’ve been able to put together already, and what we’re projected to hit by the end of the year, watching that grow exponentially is exciting not just for me as a product manager but for everyone else in the partner ecosystem and the engineering side. 

BIZTECH: What are you projected to hit by the end of the year? 

BREARD: First, I’ll say it’s never enough. There’s always more that we can do, but optimistically, we think we’ll be in the six figures of fixes by the end of the year, and well beyond that in Q1 and Q2 of next year. Time will tell. Proof is doing, not just the projection, but right now we’re slightly ahead of schedule. That’s what you want to see.  

BIZTECH: Can you compare that with prior numbers? 

BREARD: It’s hard to compare because we’ve never had an offering in this space. To be frank, you can use AI to do wonderful, amazing things, and you can use it as a bad actor. So, everything we’re doing is heavily leveraging AI in this offering, using it as best we can to stay ahead of the bad actors who are also using it in this space. That alone has let us go so far, so fast in a short amount of time, which is really encouraging to me and makes me very optimistic. It’s about the future and not needing 12 to 18 months to plan something, much less execute it. To drop that down to just a few weeks — this is the future we want to build, right? 


Photography by Trevor Paulhus
Close

New Research from CDW Explores AI and Cybersecurity

Learn how AI is helping IT teams manage risk and improve resilience.